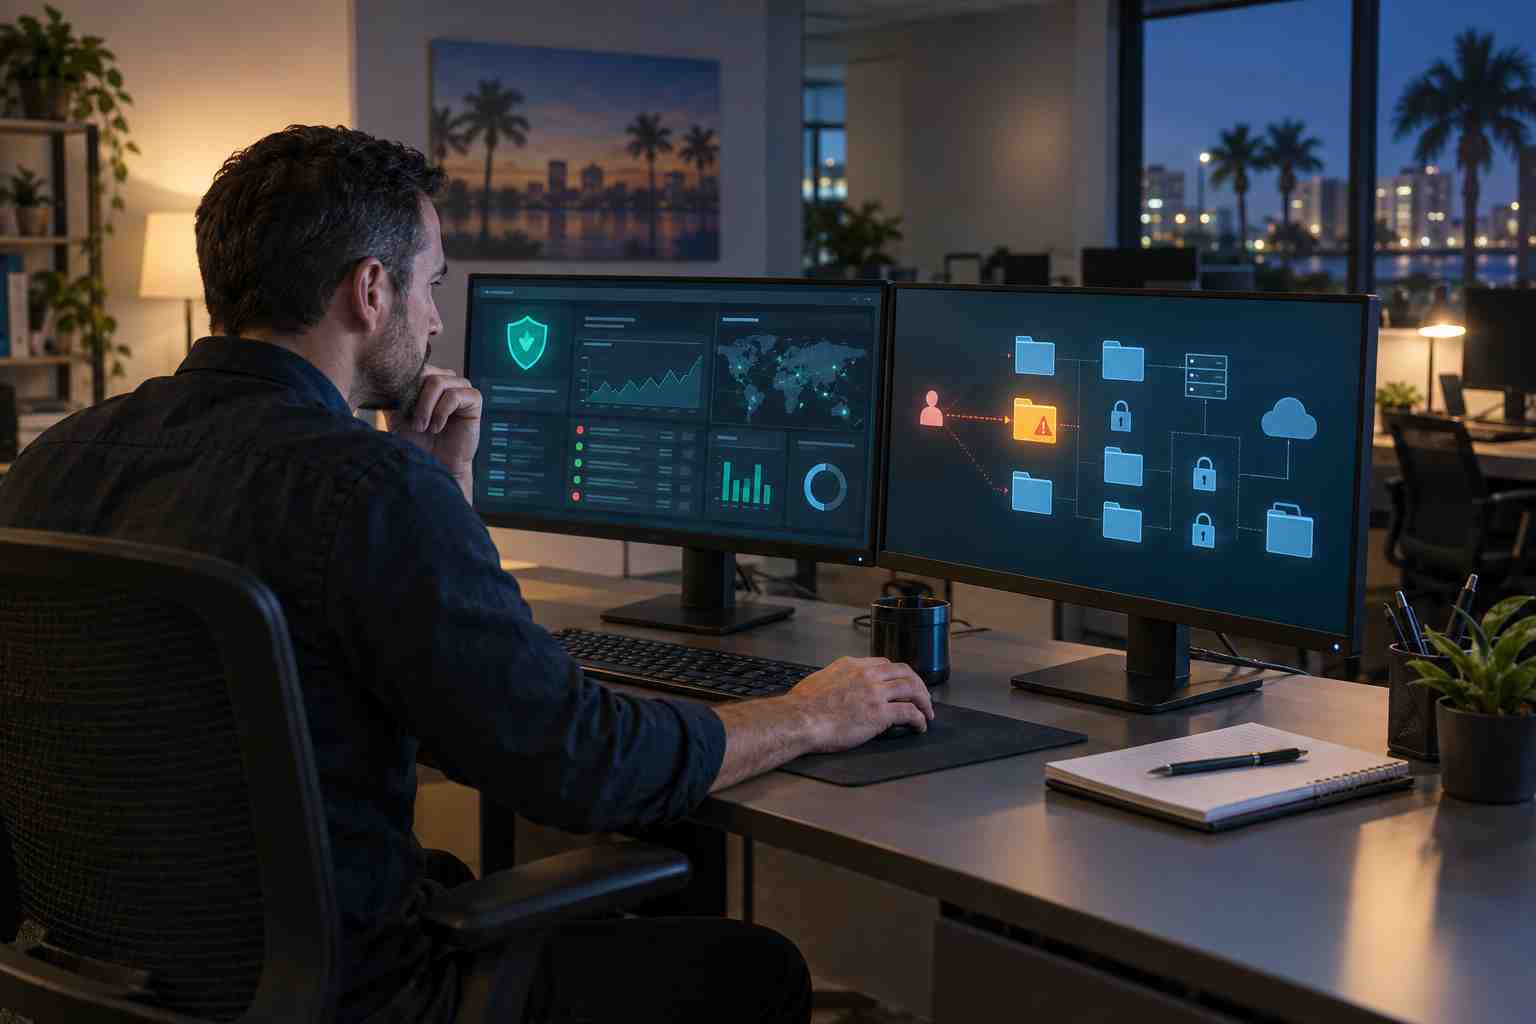
Many security tools are designed to stop obviously malicious files, suspicious websites, or known attack methods.
The harder problem begins when an intruder obtains a real employee password or gains access to a legitimate computer. Their activity may initially resemble normal work: opening folders, reviewing accounts, using built-in Windows tools, or searching for valuable information.
On September 16, 2026, the Cybersecurity and Infrastructure Security Agency released new guidance on using cyber decoys to detect that kind of activity.
A cyber decoy is a fake but realistic-looking file, account, credential, service, or system created for defensive purposes. Nobody conducting legitimate business should interact with it. If someone does, the business receives a high-priority warning that deserves investigation.
Think of a cyber decoy as a monitored door that employees have no reason to open.
The door may look real, but it does not lead to important business information. Its purpose is to reveal someone who is exploring places they should not be.
CISA’s guidance discusses several related ideas:
Small-business owners do not need to memorize these terms. The practical idea is that security teams can create something no legitimate employee should use, then treat any interaction with it as a strong warning.
CISA says many organizations struggle to detect intruders who use legitimate credentials and normal administrative tools.
Traditional security alerts can also be noisy. A tool may produce hundreds of warnings, many of which turn out to be harmless. That makes it harder for a small IT team to recognize the one event that truly matters.
A properly designed decoy can produce a clearer signal. If no employee or business application should ever open a particular file or use a particular account, activity involving that asset is difficult to explain as normal work.
CISA describes cyber decoys as a way to support continuous monitoring, create higher-confidence alerts, reduce alert fatigue, and identify activity that happens after an initial compromise.
A small business probably does not need an elaborate fake network.
A qualified IT or cybersecurity provider might instead consider a carefully controlled example such as:
The design matters. A decoy should not contain real sensitive information, interfere with normal work, confuse employees, or create a new route into the network.
Someone must also be responsible for receiving, testing, and responding to the alert. A warning that nobody sees provides little protection.
Cyber decoys are an additional detection layer, not a shortcut around fundamental security work.
Before investing in an advanced decoy program, a small business should have the basics under control:
A business struggling with shared passwords, unsupported computers, or untested backups should generally address those weaknesses first.
Decoys become most useful when the company already has someone capable of investigating the alert and containing a possible intrusion.
Business owners do not need to design cyber decoys themselves. They should understand what they are buying and how it will be managed.
Useful questions include:
Start with one narrow, testable use case. Confirm that the alert reaches the right person and that the response process works before expanding the program.
Interaction with a cyber decoy should not automatically be treated as proof of a major breach. A configuration error or authorized security test may be responsible.
It should, however, trigger prompt investigation.
The security team may need to determine:
These decisions should be handled by qualified personnel. Employees should not confront a suspected intruder, delete evidence, or attempt to investigate company systems on their own.
CISA’s guidance makes an important point: preventing every attempted intrusion is difficult, so businesses also need reliable ways to notice when somebody has slipped through.
A carefully managed decoy may help expose an intruder whose actions would otherwise blend into normal activity. For a small business, the goal is not to build an elaborate trap. It is to create one more dependable signal and ensure somebody is ready to act when it appears.


 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.