An employee receives a call or text from someone claiming to be with IT. The caller says the company is updating passkeys, multifactor authentication, or single sign-on and that the employee must act immediately to avoid losing access.
The request sounds plausible. Passkeys and MFA are real security tools, and employees have become accustomed to occasional login changes.
That familiarity is exactly what makes this tactic effective.
Microsoft reported in September 2026 that attackers have been using passkey-themed messages, personal phone calls, and convincing sign-in pages to gain access to cloud accounts. The passkey technology was not broken. Instead, criminals used the language of security as a believable reason to guide employees through a fraudulent sign-in process.
The approach may begin with:
The attacker may stay on the phone and walk the employee through each step. That personal attention can make the request feel more legitimate than an ordinary phishing email.
Some attacks use a fake page positioned between the employee and the real Microsoft login. Others persuade the employee to authorize a device that belongs to the attacker. In plain language, the criminal is trying to turn the employee’s legitimate approval into access for someone else.
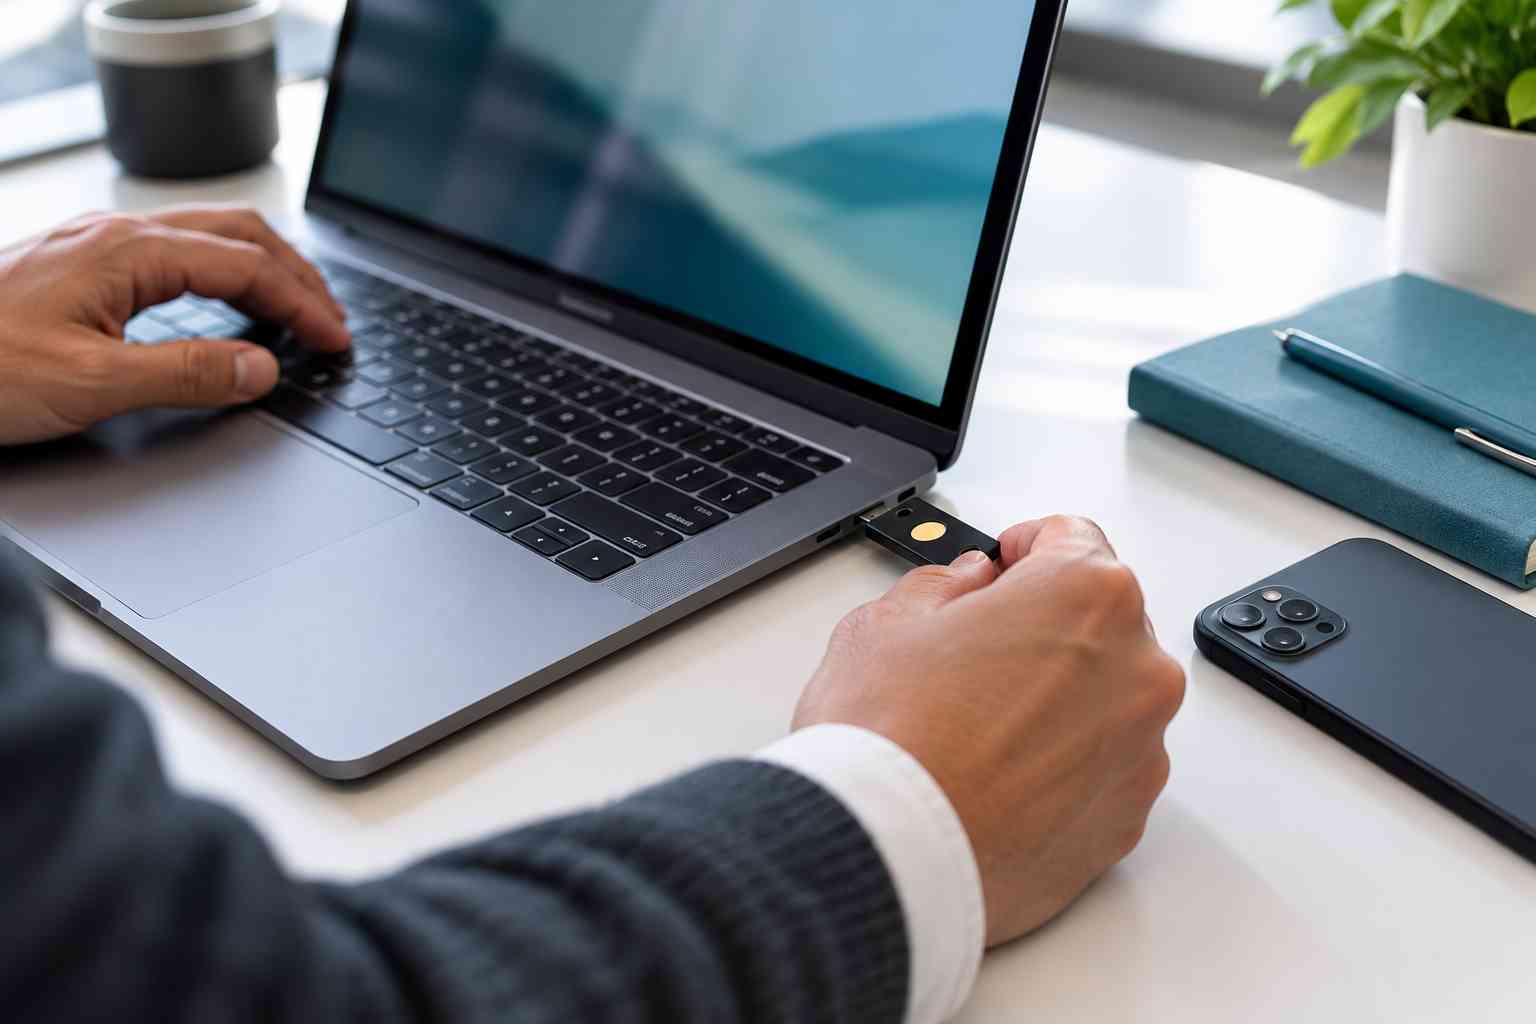
Multifactor authentication remains an important safeguard. CISA recommends requiring MFA for business accounts and moving toward phishing-resistant options such as security keys and properly configured passkeys.
However, not every form of MFA provides the same protection.
A text-message code can be shared. A push notification can be approved by mistake. Even a real Microsoft prompt can become dangerous when an attacker has manipulated the employee into approving the wrong request.
That is why businesses need both strong technology and a clear verification process.
Employees should never complete an unexpected password reset, passkey enrollment, MFA change, or device authorization merely because someone called or texted them.
Instead:
Employees should not use the callback number or contact details supplied in the suspicious message. Those may lead straight back to the attacker.
A business can reduce confusion by establishing a predictable account-support process.
Employees should know:
This process should also apply to executives. Owners, finance employees, administrators, and IT personnel are particularly attractive targets because their accounts may provide access to payments, sensitive email, customer records, or company-wide settings.
Ask your IT provider to review whether the business can:
These controls help prevent one convincing phone call from becoming unrestricted access to email, OneDrive, SharePoint, or other cloud systems.
Treat the event as an urgent account-security issue, even if the employee did not reveal a password.
Contact your IT provider immediately. The response may need to include disabling the affected account temporarily, ending active sessions, removing unauthorized authentication methods, changing the password through a trusted process, and reviewing mailbox and file activity.
Employees should not feel embarrassed about reporting the incident. Fast, honest reporting gives the business the best chance to contain it.
Passkeys and phishing-resistant MFA can provide stronger account protection, but employees must know when an enrollment request is real. A surprise caller should never be allowed to define the process.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.