A ransomware attack does not always begin with an obviously malicious attachment. It may begin with a weak password, an old remote-access account, an unpatched firewall, or a backup system nobody has tested recently.
On October 20, 2026, CISA, the FBI, the U.S. Secret Service, and international partners released a joint advisory about SafePay ransomware. The agencies report that SafePay has affected at least 600 organizations across multiple regions and has been among the most active ransomware groups of 2026.
The advisory is technical, but its message for a small business is straightforward: criminals are still finding success through preventable weaknesses.
According to the advisory, SafePay operators have used several routes into their victims’ systems:
After entering a network, the attackers may create or take over accounts, disable security protections, copy business data, delete reachable backups, and encrypt files.
This creates two separate business problems. The company may lose access to its systems, and sensitive data may be taken before the encryption begins.
Ransomware does not need to affect every computer to interrupt a business.
One compromised administrator account could give an attacker access to shared files, accounting records, customer information, scheduling systems, or connected backups. Employees may be unable to work while the company determines what was accessed and which systems can be trusted.
For an Orlando-area small business, that could mean canceled appointments, delayed invoices, interrupted customer service, or an office that cannot operate normally for days.
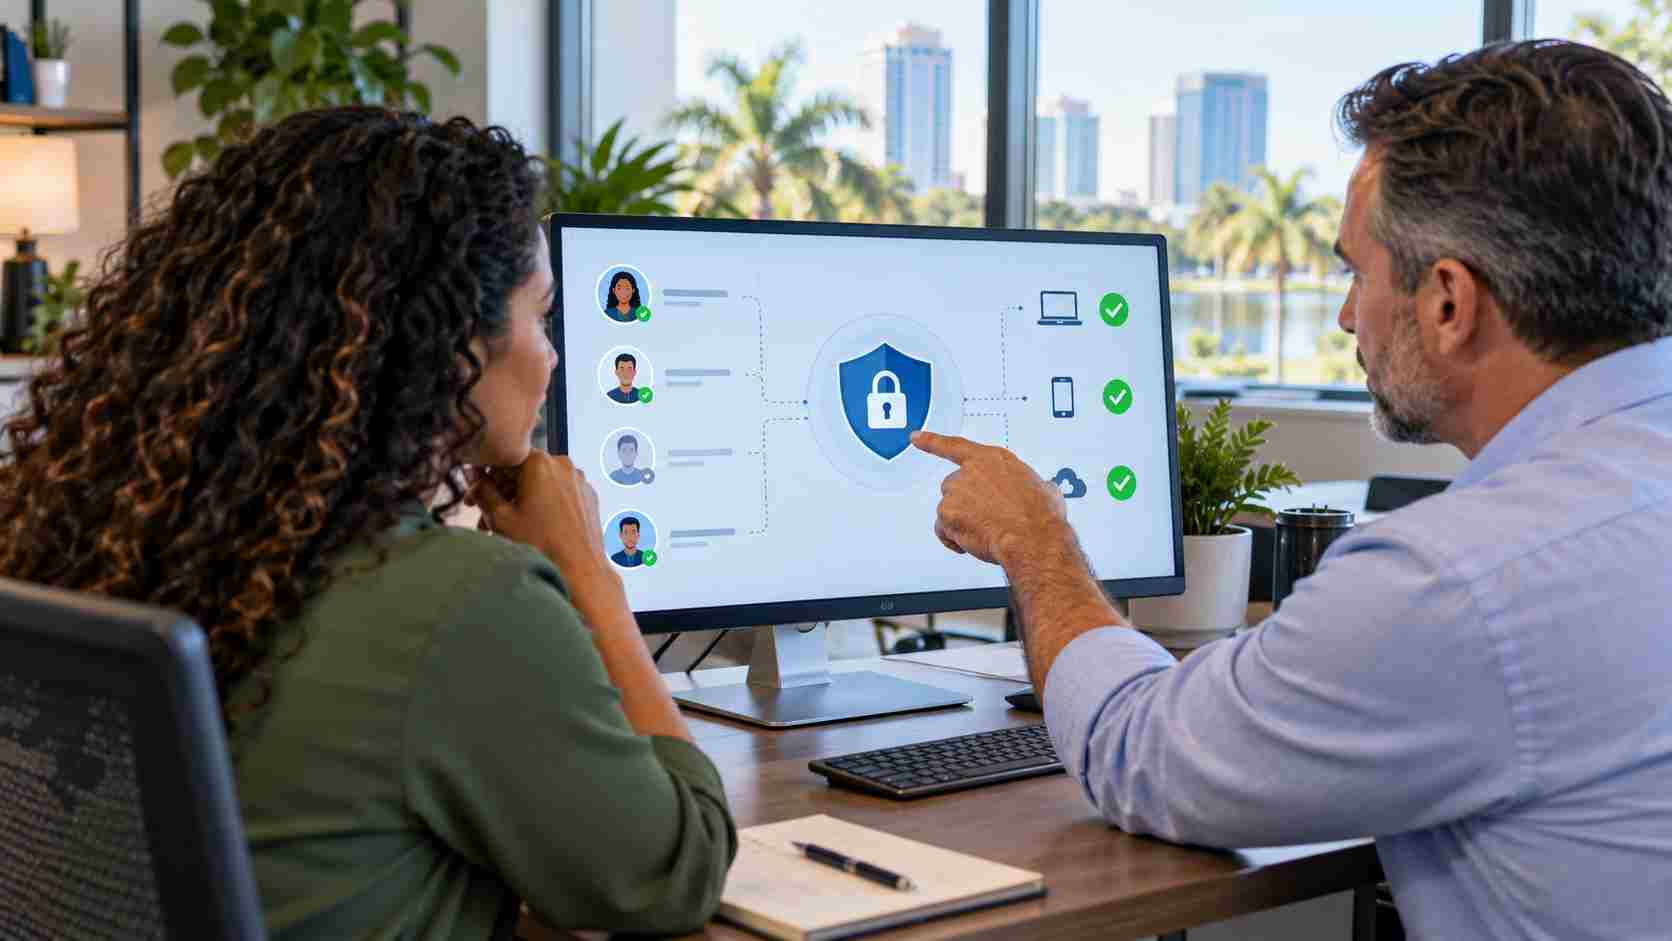
Multifactor authentication requires something beyond a password, such as an approved authenticator or security key.
CISA recommends using it for services including webmail, VPN connections, and accounts that access critical systems. It is especially important for administrators and anyone who can connect to the business network remotely.
The company should also confirm that old remote-access accounts have been disabled. An account created for a former employee, vendor, or temporary project can remain an unnoticed entry point.
A long password is helpful, but it should also be unique.
When an employee reuses the same password for several services, a breach at one service can expose the others. A business password manager can generate and store unique passwords without expecting employees to remember every one.
Shared administrator passwords should be eliminated wherever possible. Each person should use an individual account so access can be removed and activity can be reviewed.
Firewalls, VPN equipment, remote-access software, servers, and other systems exposed to the internet deserve urgent attention when security updates become available.
Small businesses should maintain an inventory of these systems and know who is responsible for updating each one. Assuming that a vendor, employee, or outside provider is handling updates is not the same as confirming that the work was completed.
Employees should not receive administrator-level access simply because it is convenient.
Ask your IT provider to review:
Reducing unnecessary access limits what a stolen account can do.
SafePay operators have used legitimate remote-control products during attacks. These programs also have valid business uses, so their presence does not automatically mean a computer is compromised.
The important question is whether every installed remote-support tool is known, approved, secured, and monitored.
An unexpected remote-control application, unexplained account, or security tool that suddenly becomes disabled should be investigated promptly.
A backup is only useful when it survives the incident and can restore the business’s data.
CISA recommends offline or otherwise protected backups, including copies that cannot be changed or deleted from an ordinary employee or administrator account. The agency also reports that SafePay has deleted network-connected backups in some incidents.
Businesses should verify:
A successful backup notification does not prove that the company can recover. A supervised restoration test does.
Employees should know whom to contact if a computer displays a ransom note, security software becomes disabled, files suddenly change, or an unfamiliar remote-access program appears.
If a possible compromise is discovered, disconnecting the affected device from the network can help limit further activity. Avoid deleting files, resetting the computer, or improvising a cleanup before an experienced response team has reviewed the situation.
The response plan should include internal contacts, the IT provider, cyber-insurance contact information, backup responsibilities, and a current list of critical systems.
Ransomware prevention is less about recognizing one criminal group and more about closing the routes that many groups repeatedly use.
Strong account protection, maintained systems, restricted remote access, monitored computers, and recoverable backups give a small business several chances to stop an attack before it becomes a full operational crisis.
Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.