An Outlook zero-day vulnerability is being actively exploited, according to Microsoft. The flaw, identified as CVE-2026-124194, was addressed in Microsoft’s November 10, 2026 security release.
A zero-day is a security weakness attackers began using before most organizations had time to install a fix. That does not mean every Outlook user has been attacked, but it does make installing the update more urgent than leaving it for an unspecified “later.”
For small businesses, Outlook is often connected to nearly every part of the operation: customer conversations, invoices, contracts, calendars, internal files, and Microsoft 365 accounts. A problem that begins with one email can therefore reach far beyond a single inbox.
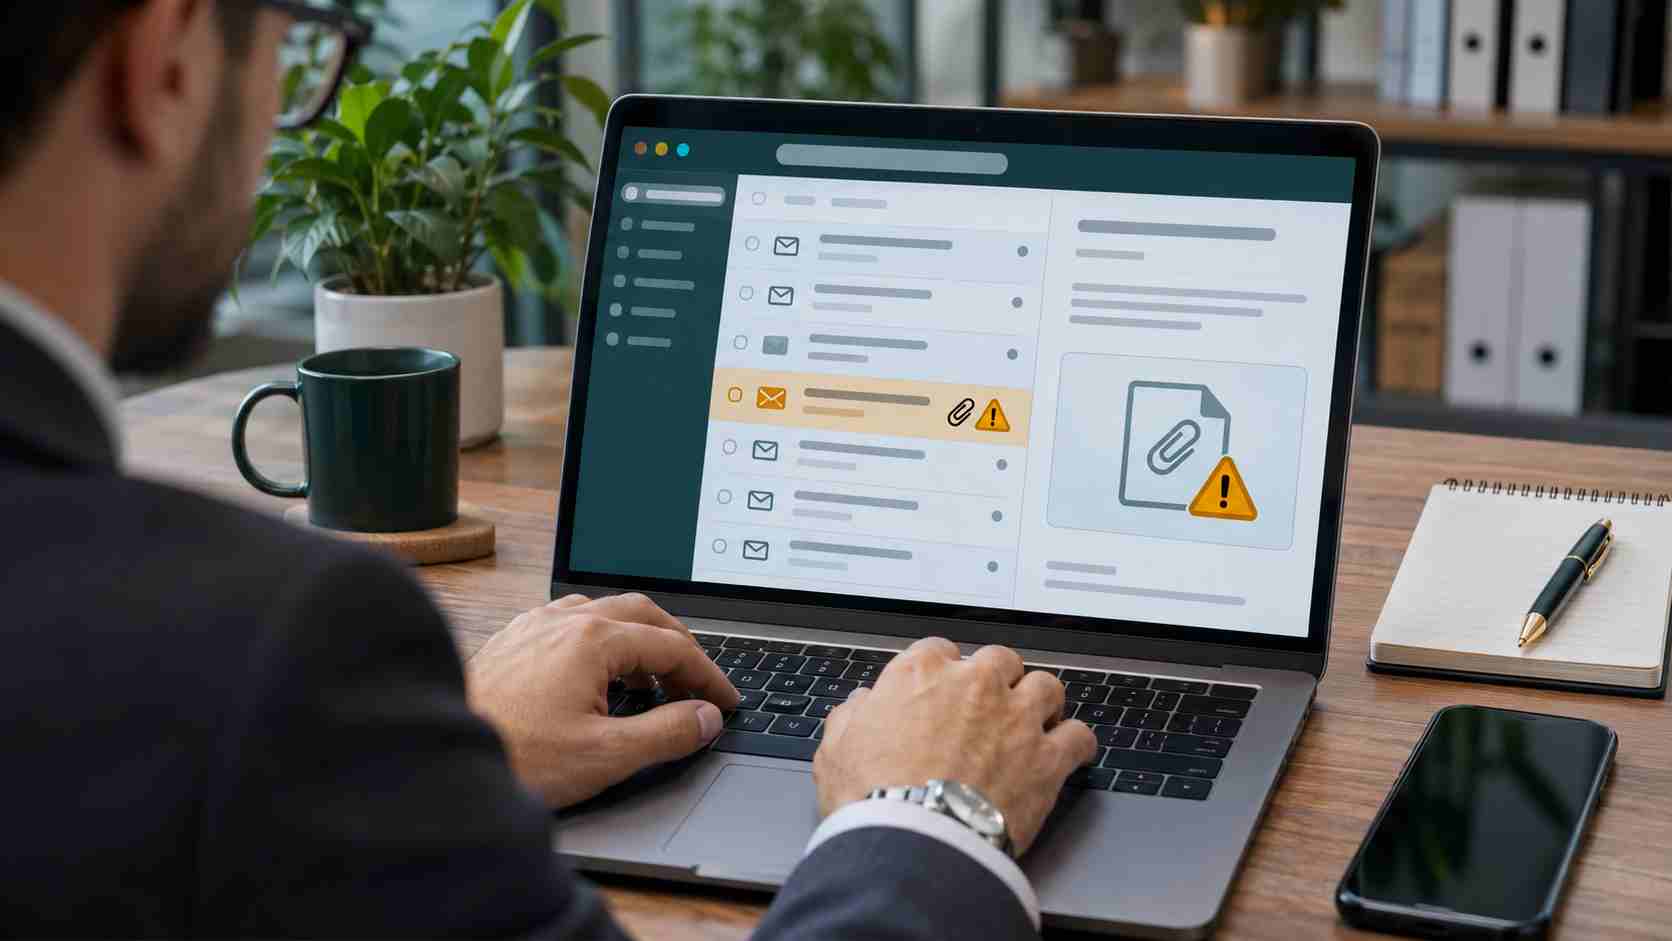
Microsoft describes the issue as an Outlook spoofing vulnerability. Available advisories indicate that an attacker can prepare a malicious file that causes Outlook to expose Windows authentication information when a user opens it.
In plain language, an attacker may try to disguise a dangerous file as something routine, such as a document, message, invoice, or business request. If the recipient opens it, the file may reveal information that could help the attacker impersonate that user or access additional resources.
This is not a reason to stop using Outlook. It is a reason to update the affected Office applications and remind employees that familiar-looking files are not automatically safe.
Microsoft reports that the vulnerability has already been exploited, and CISA has added it to the agency’s Known Exploited Vulnerabilities catalog. The November release also covers Windows, Office, SharePoint Server, Exchange Server, SQL Server, and other Microsoft products.
A stolen or compromised account can create several business problems:
Small businesses are particularly vulnerable when updates are handled inconsistently. One employee may have a fully updated Microsoft 365 installation while another computer quietly remains several releases behind.
Install the November 2026 security updates on computers running affected Microsoft 365 Apps or supported Office LTSC editions. Do not assume every computer updated successfully simply because automatic updates are enabled.
An IT administrator should verify update status across the business rather than checking only one workstation.
Updates sometimes remain incomplete until the affected application or computer has restarted. Ask employees to save their work and complete any pending restart instead of postponing it repeatedly.
Employees should slow down when an attachment is unexpected, even if the message appears to come from a customer, coworker, vendor, or manager.
Before opening it, confirm the request through a known phone number or a separate message. Be especially cautious with unusual Outlook message files, unsolicited Office documents, payment requests, or attachments accompanied by urgent language.
Employees generally should not work from accounts with full administrator rights. Limiting privileges can reduce what an attacker can change if a user or application is compromised.
Confirm that endpoint security, email filtering, and monitoring are active and reporting correctly. Multi-factor authentication remains important for overall account security, but it is not a substitute for installing this security update.
The larger lesson is that updates need an owner, a schedule, and a way to confirm completion. A patching process should cover Office applications, Windows, browsers, servers, network equipment, and other software employees depend on.
The Outlook vulnerability is serious because attackers are already using it, but the response is manageable: update affected Office installations, verify that updates completed, and remind employees to confirm unexpected attachments before opening them.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.