Cybersecurity advice often sounds as if every company has an IT department, a security team, and an unlimited budget. Most small businesses operate very differently.
On November 2, 2026, the National Institute of Standards and Technology, better known as NIST, released a new cybersecurity guide for businesses with no paid employees other than the owner. These businesses include independent consultants, contractors, solo medical and legal professionals, online sellers, and many other owner-operated firms.
Although the guide focuses on solo businesses, its plain-language recommendations are also useful for companies with a few employees and relatively simple technology.
That matters in Orlando and throughout Central Florida, where many businesses depend on one owner, several cloud services, a laptop, a phone, email, online banking, and perhaps a Wi-Fi-connected printer. A problem with any one of those systems can interrupt the entire operation.
A very small business may not have a complicated network, but it can still hold valuable information. That may include customer records, payment details, contracts, tax documents, email conversations, saved passwords, or access to a larger client’s systems.
An attack does not need to be sophisticated to cause serious trouble. A stolen email password can let a criminal impersonate the owner, redirect payments, reset other accounts, or send convincing scams to customers. A damaged laptop can bring work to a halt if important files have not been backed up.
NIST’s message is refreshingly practical: start with the technology that matters most, reduce the easiest risks, and build a plan that can grow with the business.
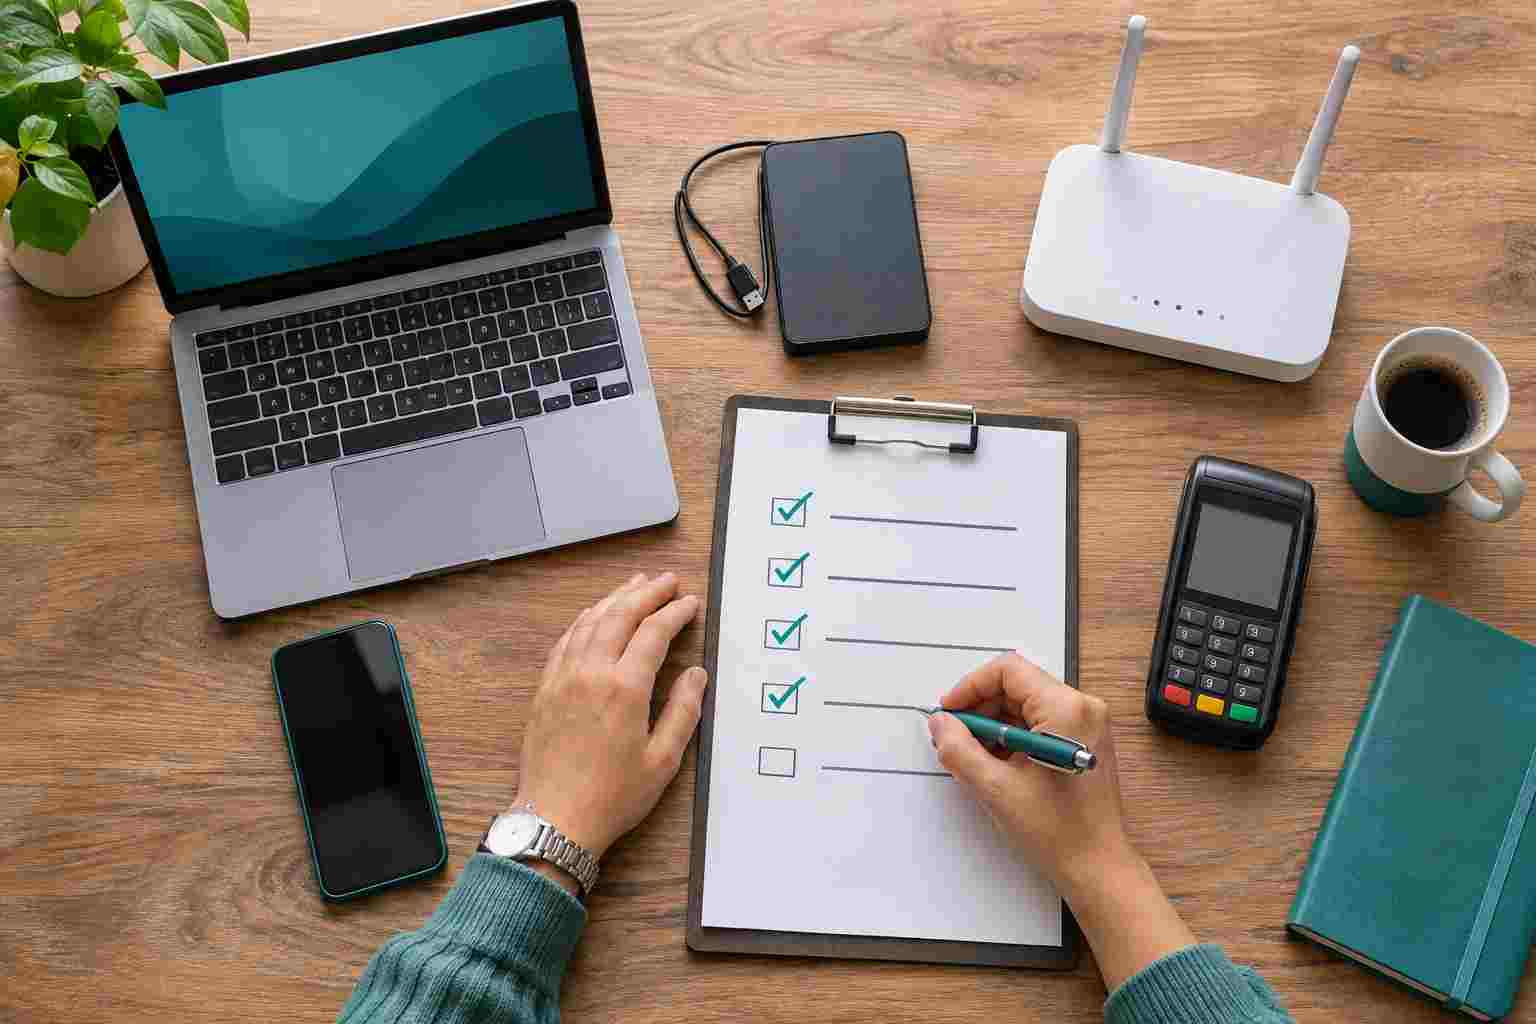
Begin with a basic inventory. You do not need specialized software or a complicated spreadsheet.
List the devices, accounts, services, and information your business relies on. Common examples include:
Then ask what would happen if each item became unavailable for a day or a week. This helps identify what deserves attention first.
NIST recommends phishing-resistant multifactor authentication for sensitive accounts. This means using a passkey, security key, or another sign-in method designed to resist fake login pages whenever the service supports it.
Start with email, banking, cloud storage, password managers, website administration, and any account that can reset other passwords.
If a stronger method is not available, conventional multifactor authentication is still better than relying on a password alone. Never approve an unexpected sign-in request, even if the notification appears legitimate.
One reused password can turn a breach at an unrelated website into access to your business email or financial accounts.
Use a reputable password manager to create and store a different password for each service. NIST’s new guide recommends passwords of at least 15 characters when passwords are required. A long passphrase is generally easier to remember and harder to guess than a short, complicated password.
Whenever passkeys are available, consider using them to reduce your dependence on passwords altogether.
Avoid performing routine work while signed in with full administrator privileges. An administrator account can install software and make major system changes, which also gives malicious software more opportunity to cause damage.
A safer setup uses a standard account for email, browsing, documents, and daily tasks. Administrative access is reserved for approved installations and system maintenance.
Updates repair security weaknesses as well as software bugs. Turn on automatic updates where practical for Windows, browsers, Microsoft 365 applications, phones, routers, and business software.
Do not forget less-visible systems such as website plugins, network appliances, payment devices, or software used only occasionally. An inventory makes these easier to track.
Business-critical updates should still be managed carefully. Testing and scheduling can prevent an update from interrupting work during a busy period.
A backup is valuable only when it contains the right information, remains protected from attackers, and can be restored successfully.
Identify the files and systems that would be difficult or impossible to recreate. Keep more than one protected copy, limit who can delete backups, and test the recovery process periodically.
Cloud storage and file synchronization can be helpful, but they are not always a complete backup strategy. Deleted, corrupted, or encrypted files may synchronize across devices.
Be suspicious of unexpected requests involving passwords, sign-in codes, invoices, gift cards, banking changes, remote support, or urgent document reviews.
Verify sensitive requests through a known phone number or a separate communication method. Do not use the contact information provided in the suspicious message itself.
Solo owners should be especially careful because there may be no coworker nearby to provide a second opinion. A brief pause and independent verification can prevent a costly mistake.
Create a short incident contact list before an emergency. Include your IT provider, financial institution, insurance contact, website provider, key software vendors, and other appropriate professional advisers.
Keep a printed copy somewhere secure. If your email or computer becomes unavailable, a contact list stored only on that device may be unreachable when you need it most.
You do not need to complete every improvement in one afternoon. Start with the systems that control money, customer information, and access to other accounts. Then address backups, updates, device security, and incident preparation.
Cybersecurity becomes much more manageable when it is treated as routine business maintenance rather than a one-time project.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.