Imagine arriving at work and discovering that employees cannot open shared files. A message on one computer demands payment. Your scheduling system is unavailable, email access is uncertain, and customers are already calling.
Who makes the first decision?
Who contacts IT? Should employees turn off their computers? Can the business keep operating? Are the backups usable? Who speaks with customers, vendors, the insurance company, or law enforcement?
Those questions are easier to answer around a conference table than during an actual emergency.
For Cybersecurity Awareness Month, Nacha’s Payments Innovation Alliance released an updated ransomware tabletop exercise kit for small and midsized businesses. The kit uses an evolving scenario, participant materials, and leadership questions to help companies discuss how they would respond. The complete exercise is designed to take approximately two to three hours, but even a shorter internal discussion can reveal important gaps. (Nacha)
A tabletop exercise is a guided conversation about a simulated incident. Nobody attacks your systems, shuts down the network, or sends a real ransom demand.
Instead, a facilitator describes a realistic situation and asks the people responsible for the business to explain what they would do next.
The purpose is not to test technical knowledge. It is to find unanswered business questions while there is still time to fix them.
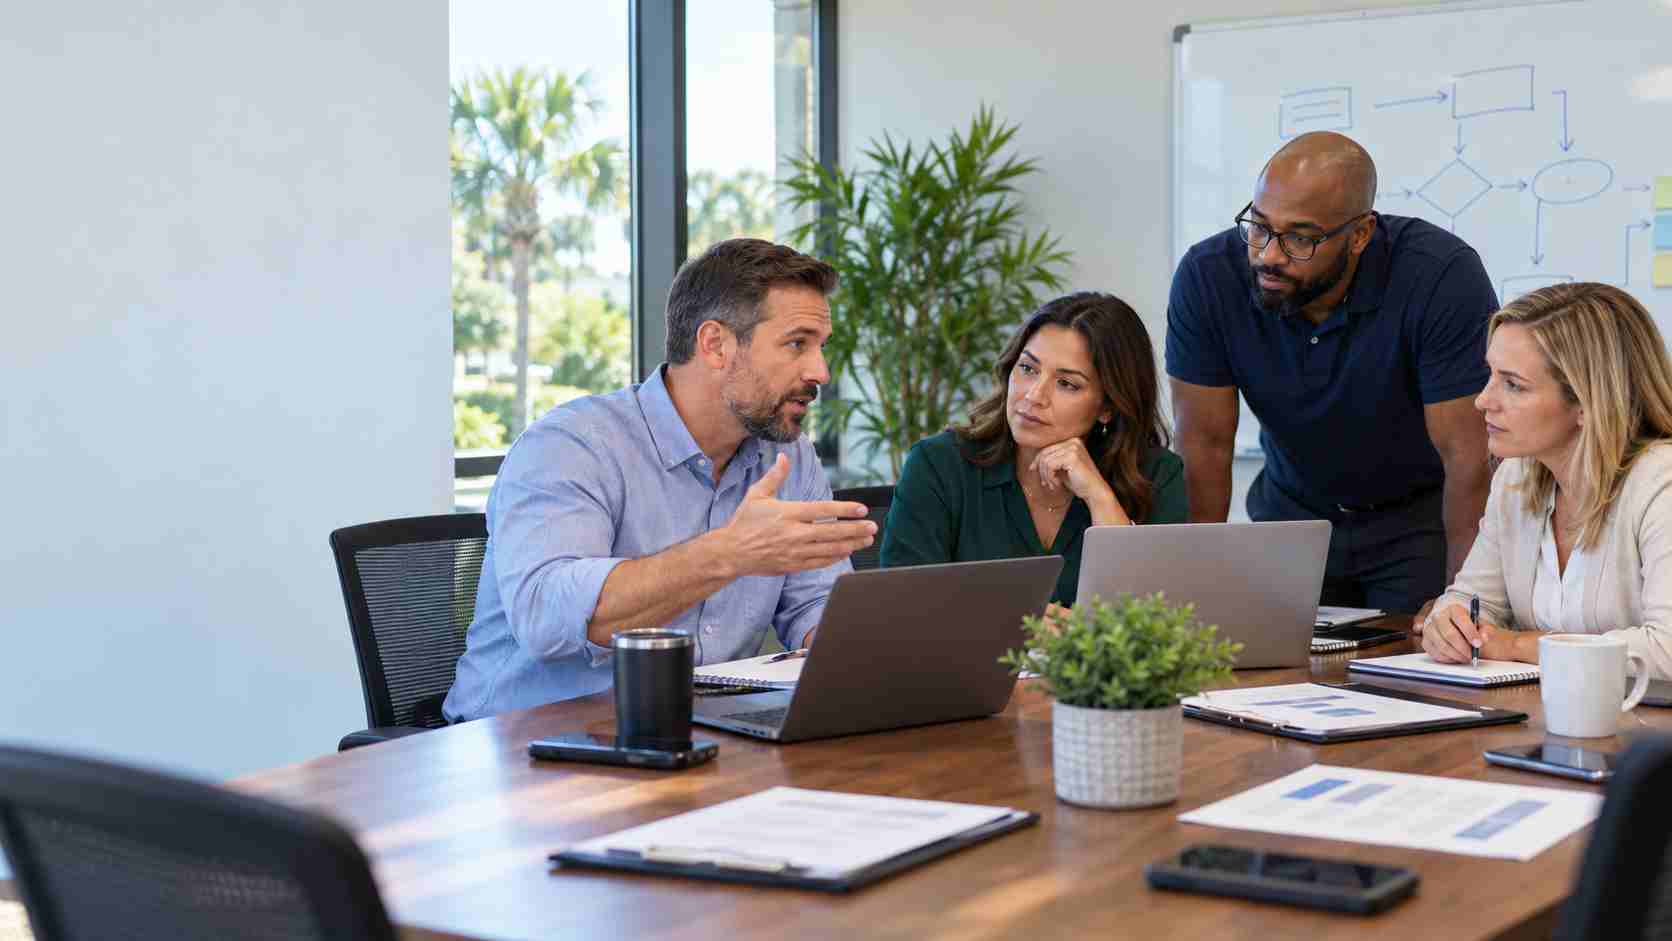
A useful exercise might include the owner, office manager, IT provider, operations lead, finance representative, and anyone responsible for customer communication. Businesses with legal, regulatory, or insurance requirements should also identify the qualified professionals they would contact during a real incident.
Start with a simple scenario: an employee reports that shared files will not open, and a suspicious message appears on a workstation.
Work through questions such as:
The goal is not to produce perfect answers during the meeting. The goal is to discover which answers are missing.
A ransomware exercise often reveals that the business depends on more systems than expected.
A company may have backups but no tested method for restoring its scheduling software. The emergency contact list may be stored in the email system that just became unavailable. Employees may know the IT provider’s name but not the correct phone number. A cloud application may work, but nobody may know whether compromised accounts should continue using it.
List the systems the business needs to perform essential work, including:
This list helps establish a sensible recovery order instead of letting the loudest problem control the response.
Technology is only part of ransomware response. People must know what they are authorized to do.
Employees should understand how to report a suspected incident without feeling blamed. Managers should know who can make operational decisions. The IT provider should have current contact information for authorized leaders. Important contacts should be available somewhere other than the affected computers.
The exercise should also confirm that nobody will negotiate, pay, delete evidence, or make public statements without appropriate professional guidance. Legal, insurance, regulatory, and notification obligations vary, so those decisions require qualified advice.
At the end of the exercise, write down the most important gaps and assign an owner and deadline to each one.
Common follow-up work may include:
The Federal Trade Commission recommends that small businesses maintain and regularly test incident-response, disaster-recovery, and business-continuity plans. CISA also provides tabletop resources that organizations can use to discuss ransomware and other threat scenarios. (FTC, CISA)
A tabletop exercise cannot prevent every attack, but it can reduce hesitation, confusion, and avoidable downtime. It gives business leaders a clearer understanding of what they depend on and what still needs attention.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.