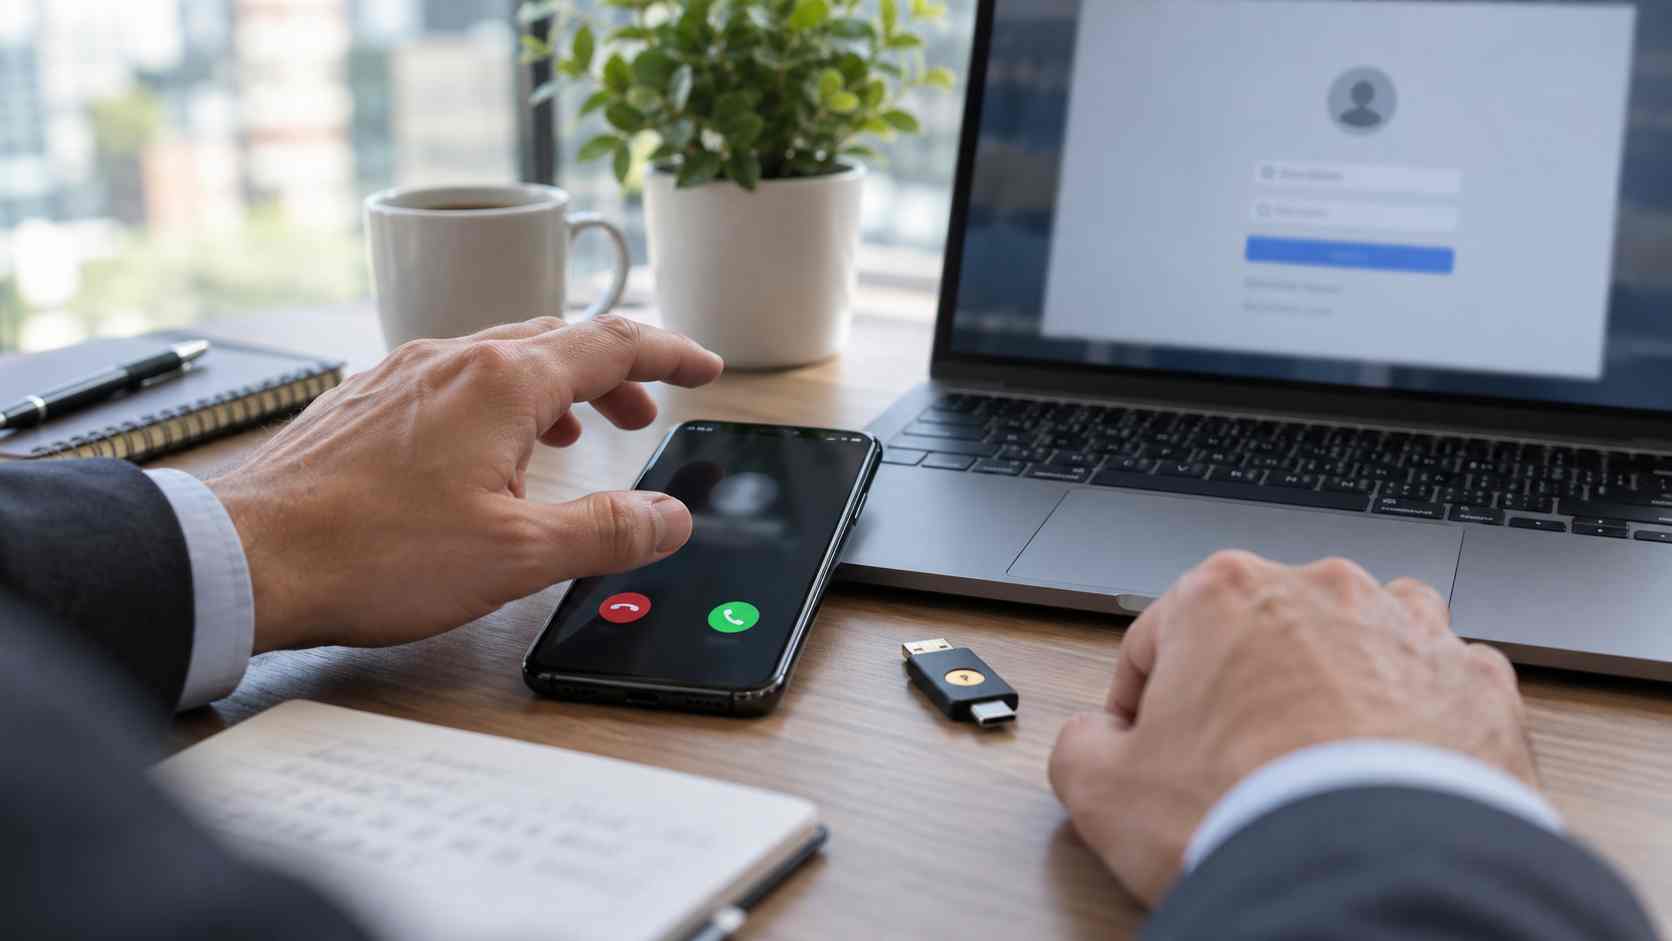
A phone call from “IT support” may feel more trustworthy than an unexpected email. The caller may know an employee’s name, title, company, and email address. They may even sound patient and professional.
That familiarity is exactly what makes a newly reported Microsoft 365 attack so dangerous.
In September 2026, Arctic Wolf described an active campaign in which criminals call business leaders while pretending to represent an internal IT department or help desk. The callers direct their targets to convincing account-registration or passkey websites. If the employee follows the instructions, the attackers may gain access to Microsoft 365 and other cloud services.
The lesson for small businesses is simple: phishing no longer arrives only through email. It can begin with a helpful-sounding phone call.
The campaign is being tracked as PREY-0058. According to Arctic Wolf, the attackers have frequently targeted directors, vice presidents, executives, and IT personnel.
The call may claim that the employee needs to:
The caller then sends or dictates a website address that appears to relate to the company or Microsoft 365. The page is controlled by the attacker, even if it looks like a normal sign-in screen.
When the victim enters a password and approves a verification request, the attacker may capture enough information to take over the active cloud session. This can let the criminal access email, SharePoint sites, OneDrive files, and other connected services.
Multifactor authentication, often called MFA, is still an important security control. It normally requires something beyond a password, such as an app approval, security key, or device-based confirmation.
The problem arises when an employee is persuaded to approve the attacker’s sign-in.
In this campaign, the criminal is not necessarily breaking the MFA system. The attacker is manipulating the person into completing the authentication process for them.
That is why unexpected verification requests should never be approved simply because someone on the phone says they are from IT.
Businesses should also work toward phishing-resistant sign-in methods, such as properly configured passkeys or physical security keys. These methods can provide stronger protection against fake login pages, but they still require careful setup and clear employee instructions.
Executives and managers often have access to more information than an average employee. Their accounts may contain contracts, employee records, financial discussions, customer information, strategic documents, or confidential email.
They are also busy. A convincing caller who creates urgency may be able to pressure an executive into acting before checking the request.
Small companies are not immune. In a smaller Orlando business, one owner or office manager may have access to nearly every shared document, mailbox, vendor relationship, and financial workflow.
A compromised account may therefore expose a large portion of the company’s information without the attacker ever installing traditional malware.
Every business should adopt one clear rule:
Employees should independently verify unexpected requests involving passwords, passkeys, MFA, remote access, or account changes.
That means ending the call and contacting the real IT provider through a known number, support portal, or previously saved contact.
Do not use a telephone number, website, or contact method supplied by the unexpected caller. Caller ID is not enough because displayed numbers and names can be misleading.
Employees should understand that pausing to verify a request is not rude or uncooperative. It is the correct security response.
Treat a support call as suspicious when the caller:
A legitimate technician should be comfortable with independent verification.
First, tell employees that criminals may impersonate internal IT staff by phone, text message, or collaboration platform.
Next, document how genuine support requests will be handled. Employees should know the official telephone number, support portal, and people authorized to request account changes.
Businesses should also review:
These controls help reduce both the likelihood and potential impact of an account compromise.
If an employee only received the call and did not follow its instructions, report the attempt internally so other staff can be warned.
If the employee visited the website, entered information, approved an authentication request, installed software, or allowed remote access, contact the company’s trusted IT provider immediately. The account, active sessions, authentication methods, email rules, file activity, and device may all need to be reviewed.
Avoid trying random fixes or deleting information that could help determine what happened.


 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.
 Trustindex verifies that the original source of the review is Google.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.