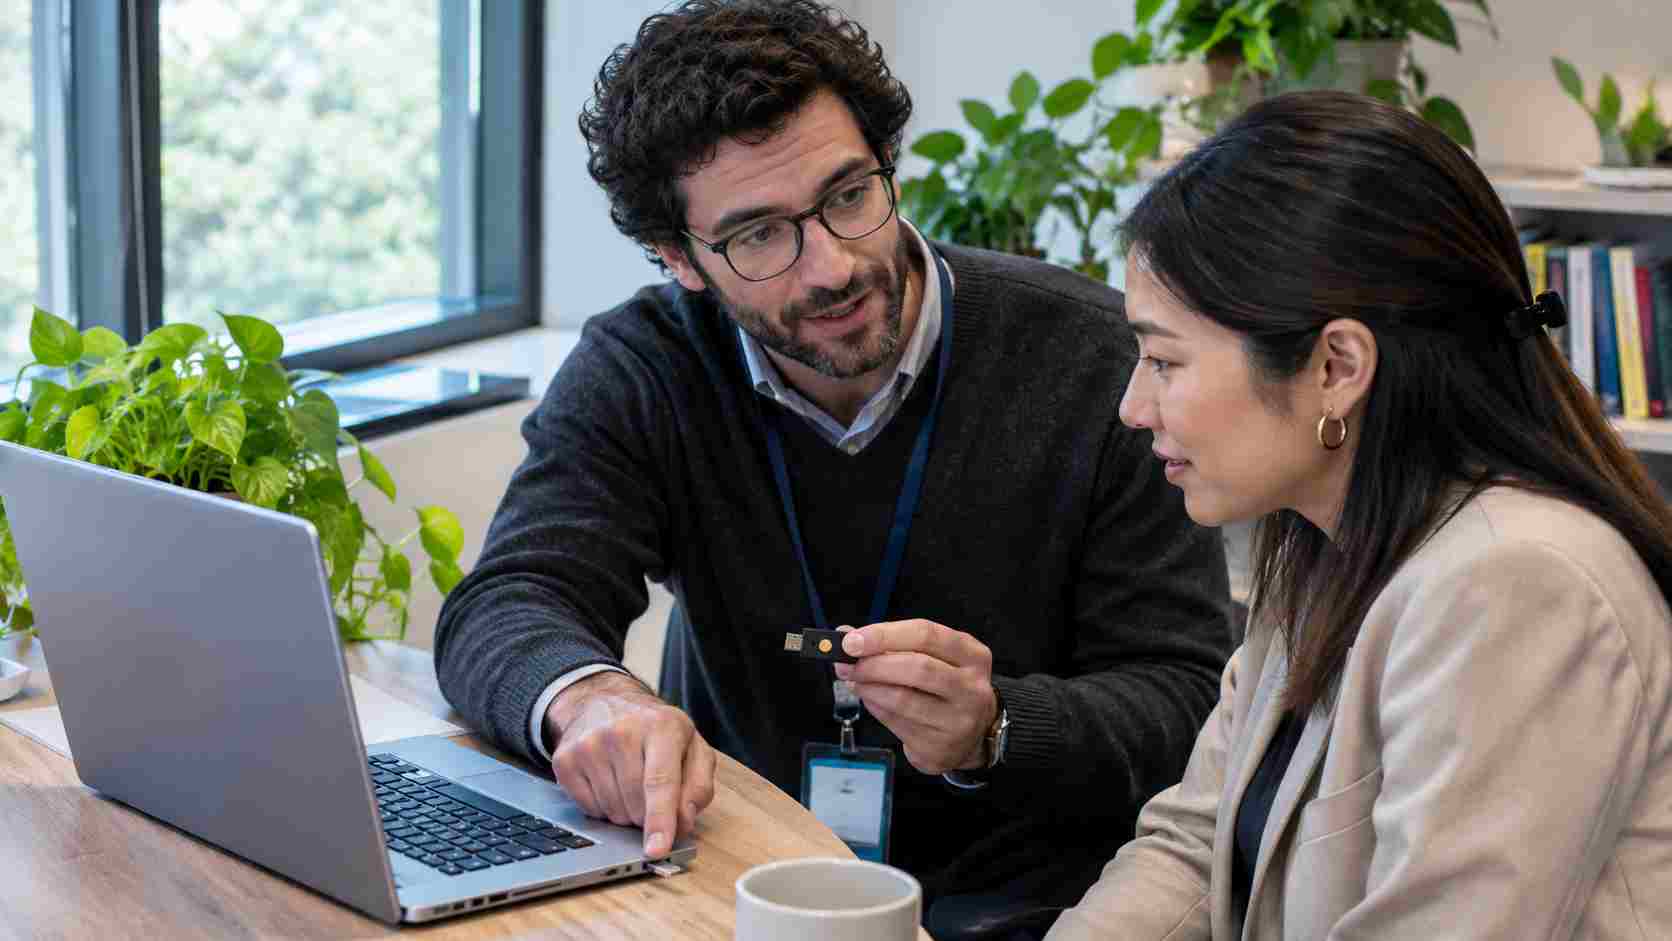
A passkey lets someone sign in using a device they already have, often by unlocking it with a fingerprint, face recognition, or a device PIN. A security key is a small physical device used to help verify a sign-in.
Both can use a standard designed to check that the sign-in is happening with the legitimate service, rather than a look-alike phishing site. CISA recommends phishing-resistant multifactor authentication, or MFA, as the strongest widely available approach for protecting accounts against phishing. CISA: Implementing Phishing-Resistant MFA
MFA simply means using more than one way to verify who is signing in. The exact experience and level of protection depend on the service and how the sign-in method is configured, so ask your IT provider to confirm what each account supports.
Imagine an employee receives a message that looks like a routine request to review a shared document. The link leads to a convincing but fake sign-in page.
With a password and a one-time code, an employee can potentially be persuaded to hand over both. A properly configured phishing-resistant sign-in method is designed to prevent that particular trick from working in the same way.
That matters because a compromised account can disrupt everyday work. An attacker may be able to read email, impersonate an employee, access documents, or attempt to redirect payments. Stronger sign-ins are one layer of protection, not a substitute for verifying unusual requests and monitoring accounts.
Begin with accounts that could cause the most disruption if someone else accessed them:
Ask your IT provider which of these services support passkeys or security keys, and which sign-in and recovery options are currently enabled.
A stronger sign-in system still needs a practical way back in when someone loses a phone or security key.
Before rollout, agree on how employees will enroll, how a replacement will be issued, and who can approve account recovery. Depending on the service, registering a second security key or another approved recovery method may help. Keep spare keys secure and follow your IT provider’s instructions.
Also review what happens when someone joins or leaves the business. Access should be assigned to the right person, reviewed regularly, and removed promptly when no longer needed.
Keep MFA enabled wherever it is available. CISA identifies authenticator-app codes or approval prompts with number matching as useful options for smaller businesses that cannot immediately adopt phishing-resistant MFA. These methods still require care because they can be vulnerable to phishing. CISA: MFA Options for Small and Medium Businesses
Tell employees not to approve a sign-in they did not start or share a code with someone who contacts them unexpectedly. When in doubt, they should contact their IT provider through a known phone number or support channel.
The right approach is the one your team can use consistently, with a sensible backup plan when something goes wrong. Start with your most important accounts, test the process with a small group, and expand as your team becomes comfortable.

Himala and his team at Cybernetic Networks have been amazing. We have been a customer of Cybernetic Networks for well over 14 years now, both personally and professionally. Himala and his team are professional, reachable and on the cutting edge of technology. We have enjoyed doing business with Cybernetic Networks for many years and still rely on their knowledge, skills and technology every day
Himala and his Cybernetic team have never let me down! For over 10 years now they have been fixing my technical issues, set up all my new networks and computers and have safeguarded me from any hackers or malware. You can trust this company to navigate you as your company grows and to keep you on track with the latest in security and safety
I am a solo practicing neurologist and have had all my IT needs covered through Cybernetic Networks since 2007. They are the best! All of their tech support staff is extremely knowledgeable and efficient. Just as importantly, they are quickly responsive whenever we need their assistance. I couldn’t be happier with their service and give them my highest recommendation!
I couldn't be happier with Cybernetics - they are experts, always respond quickly , and solves any issues I have.
Cybernetic Networks has been advising and supporting all our IT issues and purchases for the last 18 years. They are very responsive and extremely knowledgeable- always providing us with timely services.
It is not often you find small business companies that are not only rewarding to work with, but also have integrity, truth and skill. I have worked with this company for over 20 years, and the service is outstanding. I can easily recommend that if you need an IT company, this is the one to get. Full STOP! Look no further, you will be happy that you did. Sue Myhelic, Gulf Breeze Real Estate, Naples, Florida.
Himala and his team from Cybernetic Networks, Inc. has been an integral part of our successful retail business for the past 20 years. He is extraordinarily knowledgable and always available for our IT needs. Thanks to Himala and his team we are always up and running.